Skip to content
LR-Gutierrez

Full-stack engineer and team lead.

I build software where security is a design decision, not a final checklist.

Based
Caracas, UTC−4
Coding
Since 2019
Status
Open to remote and relocation
Now
Senior developer, PCI-DSS banking
Before
Information Security Manager, INAC
Stack
ASP.NET Core, NestJS, Angular, Kotlin, PostgreSQL

Selected work

02 projects

AuraOS dashboard: live occupancy against 90 bays, today's revenue, active memberships and shortcuts to branches, exits, kiosk mode and audit

Dashboard · live occupancy, revenue and shortcuts

01 · 2026

AuraOS

Local-first parking access control

Replaces the paper log at a parking lot with an app for the guard on rounds and a self-service kiosk. Keeps working offline through a custom change journal and field-level merge, syncing to a NestJS and PostgreSQL backend; operators sign in with biometrics backed by hardware keys.

  • Kotlin
  • Room
  • NestJS
  • PostgreSQL · Prisma
  • SSE · FCM
  • Android Keystore

Control panel · orders, mileage alerts, finances and inventory by period

02 · 2026

AutoNex

Workshop ERP, from vehicle intake to delivery

Service orders that record mileage, fuel level, prior damage and reported faults; a vehicle history per plate or VIN; inventory with minimum-stock control; mileage-based maintenance reminders over WhatsApp; and official BCV exchange rates scraped, approved and published on schedule.

  • ASP.NET Core
  • PostgreSQL
  • Angular
  • Ionic · Capacitor
  • SignalR
  • wa-notifier · NestJS
  • Biometric auth (mobile)

How I work

Security as a design input

I ran information security at Venezuela's civil aviation authority and now build inside a PCI-DSS banking environment. Authentication, data handling and failure modes are decided with the architecture, not audited after it.

Leading the team, not just the code

I've coordinated development teams end to end: gathering requirements with the people who use the system, planning and tracking work, and reporting progress to leadership.

AI in the development loop

I write Skills and MCP servers and orchestrate agents to speed up the repetitive parts of the cycle, while design decisions and review stay mine.

  • .NET
  • NestJS
  • Laravel
  • OpenJDK
  • JSON Web Tokens
  • Angular
  • TypeScript
  • React
  • Tailwind CSS
  • Kotlin
  • Android
  • Ionic
  • PostgreSQL
  • Prisma
  • SQLite
  • Linux
  • Proxmox
  • GNU Privacy Guard
  • WhatsApp
  • Firebase

Skills

Select one to see where I applied it

Backend

Frontend

Mobile

Data

Infrastructure

Security

Integrations

AI

Leadership

Every skill here links to a project or role where I used it. Nothing listed without evidence.

Experience

  1. Aug 2026 – nowSenior Software DeveloperP&A Asociados Gerenciales · consulting for a universal bank, PCI-DSS
  2. Mar – Aug 2026Software ConsultantFreelance · automotive workshop ERP
  3. 2025 – 2026Information Security ManagerINAC · GPG-based procedure for exchanging sensitive data with external entities
  4. 2023 – 2024Software DeveloperINAC · high-demand REST API with rate limiting, JWT and route-level permissions
  5. 2023Software DeveloperBolivariana de Aeropuertos
  6. 2022 – 2023Development & Systems CoordinatorInmobiliaria Nacional · led the development team; infrastructure on Proxmox
MSc Cybersecurity, CEUPE (expected 2027) · BEng Computer Engineering, UNEXCA

English (B2) · Russian (A1)

Open to remote roles as a senior engineer or team lead

luisangelrgr@gmail.com

01 · 2026

AuraOS

Local-first parking access control

Replaces the paper log at a parking lot with an app for the guard on rounds and a self-service kiosk. Keeps working offline through a custom change journal and field-level merge, syncing to a NestJS and PostgreSQL backend; operators sign in with biometrics backed by hardware keys.

Problem

The lot this is modeled on ran on a paper log: slow at the gate, no real history, and no way for a guard to flag something irregular. Connectivity on site is unreliable, so anything built had to keep working with the network down.

Role

Sole developer and lead on both sides: the Android client (Kotlin, MVVM, Room) and the NestJS/PostgreSQL backend. Owned the sync protocol end to end.

Constraints

  • Offline-first: the guard's device has to keep working through dead zones, with no silent data loss on reconnect.
  • No QA team — correctness has to come from the data model, not from manual testing.
  • One developer, so the sync protocol couldn't lean on a server arbitrating conflicts; it had to stay simple enough to reason about alone.

Key decisions

Field-level LWW with device timestamps

Each field merges independently, last write wins, using the timestamp the device recorded when the change happened — the server never substitutes its own clock. That keeps the client fully offline-capable and the merge logic simple. The trade-off: a device with a wrong clock can silently beat a correct edit, and DELETE resolves blind, with no negotiation if a delete and an edit race. Acceptable for an access log, not something I'd default to for financial data.

Append-only ChangeJournal

Every local mutation is recorded as an immutable entry and replayed to sync, instead of diffing mutable state. It makes the sync protocol auditable and easy to debug offline, at the cost of a growing local journal that needs periodic compaction — not yet built.

Biometric auth over a shared PIN

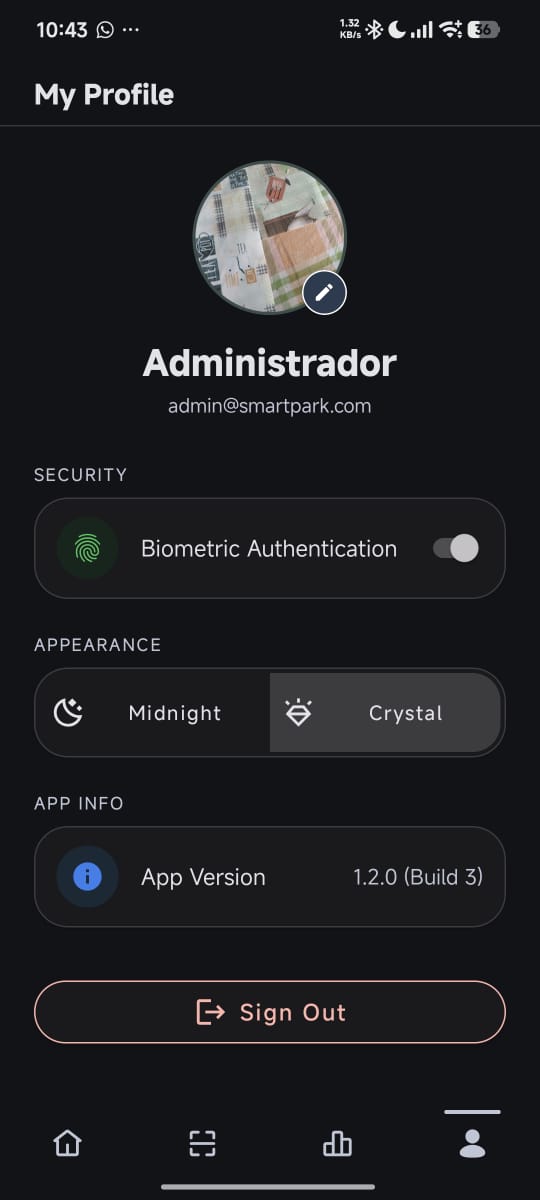
Operators share a physical device at the booth, so a PIN is effectively shared too. Biometric unlock backed by Android Keystore hardware keys ties each action to a person, not a device. Trade-off: every operator needs to enroll before their first shift.

Architecture

Kotlin, MVVM and Room on the client; a NestJS and PostgreSQL (Prisma) backend synced over SSE, with FCM for push when the app isn't in the foreground.

Outcome

A complete, documented functional prototype: both apps build and run, and the sync protocol works end to end in manual testing. It hasn't been deployed or tested against real field conditions, there's no CI, and some tests are currently failing — closing those out comes before any pilot, not after.

What I'd do differently

I'd set up a CI job from day one, even just lint and build on push, instead of leaving it for later. And I'd revisit the blind DELETE resolution before this reaches a real site: a soft-delete with explicit conflict surfacing is a small change now and a much bigger one once there's real data to migrate.

Stack

  • Kotlin
  • Room
  • NestJS
  • PostgreSQL · Prisma
  • SSE · FCM
  • Android Keystore